Blog
Data Security Engineering: Building Protection Into the Life Cycle, Not After the Breach
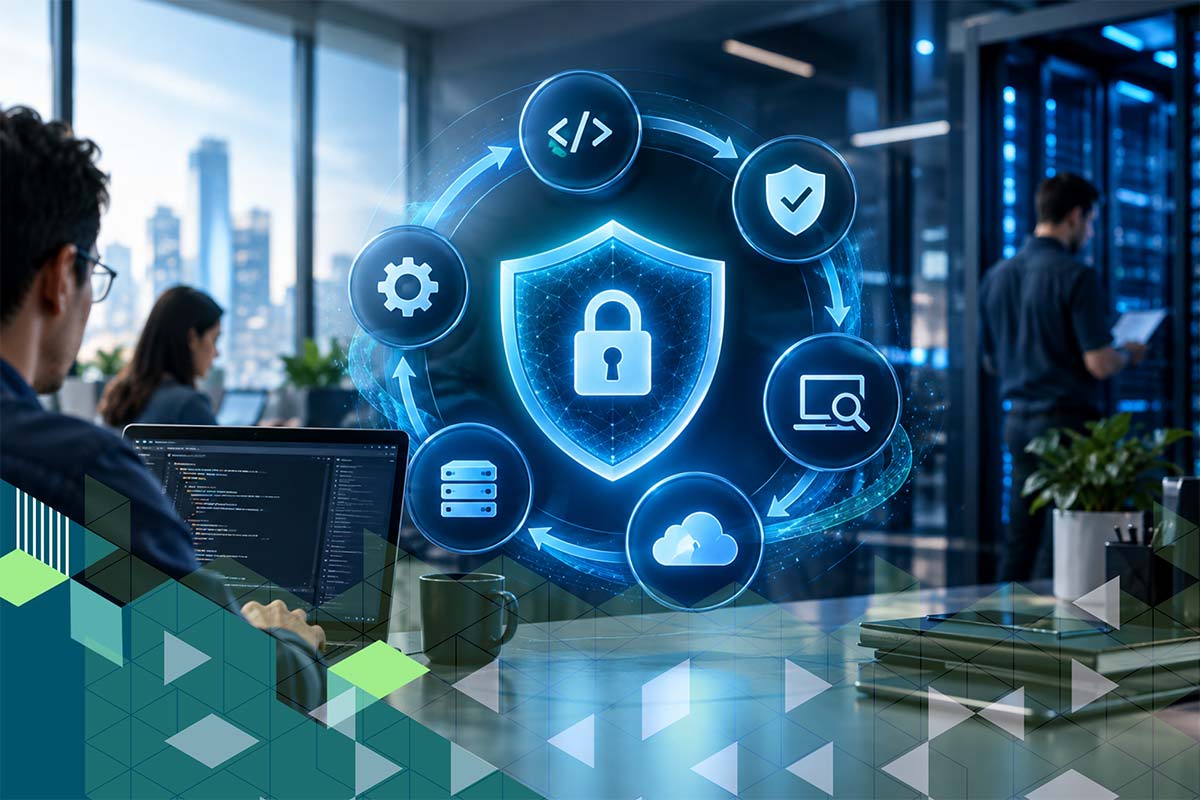
Data Security Engineering Starts at the Dataset Build
Most data protection programs begin at the wrong moment. Controls arrive after a dataset is already built, already in use, and already exposed. Data security engineering moves the starting line. It integrates visibility and access controls into the dataset build process forward, treating protection as a property of the data itself rather than a layer added later.
The discipline follows a shift-left principle. Security measures are provisioned from the earliest stages of the data life cycle, so sensitive information is governed from the moment it enters an environment. Classification, encryption, and access rules become part of how a dataset is created, not a project scheduled for after something goes wrong.
The stakes are measurable. The IBM Cost of a Data Breach Report 2025 put the global average breach at $4.44 million, with organizations taking a mean of 241 days to identify and contain an incident. Every one of those days is time sensitive data sits unprotected. Building controls in at the source shortens that window before it ever opens.
The Cost and Risk of Retrofitting Controls After a Breach
Retrofitting is expensive by design. Fixing a problem late means unwinding decisions already baked into production systems, then rebuilding around them under pressure. The economics are well documented in software engineering, and they apply directly to data. NIST-referenced research found that remediating a flaw in production costs roughly 30 times more than catching it during development. Black Duck's analysis of IBM Systems Sciences Institute data found defects fixed at the implementation stage cost 6 times more than those caught at design, and the multiplier climbs steeply from there.
The risk compounds alongside the cost. Retrofitted controls are applied to environments that were never structured to hold them, which leaves seams. The 2025 breach cost report found that 97% of organizations that suffered an AI-related breach lacked proper access controls, a direct consequence of protection arriving after systems went live. Late controls also carry a heavier operational tax. Teams rebuild pipelines, re-permission users, and re-audit data that should have been governed from the start.
Post-incident remediation adds one more penalty. It happens during a breach, when attention, budget, and goodwill are already spent on containment.
Five Plays as One Data Protection System
Data security engineering runs on five plays, and their value comes from operating as one system rather than five separate initiatives.
Data Classification and Categorization
Establishes what data is sensitive and who is permitted to reach it. Classification without enforcement is a label, and enforcement without classification is a guess, so the two work as a pair.
Data Visibility
Provides continuous awareness of where sensitive data lives across cloud sources, on-premise stores, databases, and data lakes. Nothing downstream can protect data that has not first been discovered.
Access Controls
Governs entitlement at the point of use, enforcing least-privilege access so that visibility translates into restriction, not just observation.
Security Policies and Standards
Turns individual decisions into repeatable rules. Centralized, enforced policy is what keeps protection consistent across teams and environments instead of varying by whoever built the pipeline.
Remediation
Closes the loop by monitoring for exposure, prioritizing what matters, and driving remediation before an issue becomes an incident.
Run in isolation, each play leaves a seam. Run together, they form a single protective fabric that covers the data from build to disposal.
Data Handling as the Operational Layer
The five plays describe what protection looks like. Data handling is how it runs day to day. It is the operational layer that turns strategy into a continuous cycle of four repeating actions.
- Tag identifies and labels PII, PCI, and PHI content, tying protection to user consent and access restrictions at the field level.
- Protect enforces encryption and controlled access on sensitive data, so the baseline defense travels with the data instead of depending on its location.
- Report monitors trends and drives response to incidents, feeding what it learns back into the protect, tag, and dispose steps.
- Dispose archives historical data and deletes what is no longer needed, shrinking the attack surface by ensuring data does not outlive its purpose.
Protect, tag, dispose, and report run as one continuous loop, not a checklist completed once. Each turn of the cycle informs the next, which is what keeps controls current as data volumes and regulations change.
The Dual Return: Fewer Incidents, More Productive Data Teams
Building protection into the life cycle pays back on two fronts at once, and this is where Amiseq's data security engineering practice is designed to deliver.
The first return is fewer incidents. When classification, access, and disposal are provisioned at the build stage, the exposure windows that drive breach cost and lifecycle duration close before they open. The 2025 report on breach costs ties both breach cost and containment time directly to how early and how well controls are in place, which is exactly the lever early-stage engineering pulls.
The second return is more productive data teams. Governed data is easier to work with. When access is clear, classification is trusted, and policy is consistent, data workers spend less time chasing permissions and validating provenance and more time on analysis and delivery. Amiseq builds data security engineering so protection and productivity move together, using discovery, classification, and policy enforcement to give teams complete visibility and control without slowing them down.
Security framed as a build discipline stops being a tax on the data team and becomes part of what makes the team faster.
How Amiseq Extends the Discipline Into AI Data Pipelines
AI raises the stakes on every principle above. Models are only as trustworthy as the data feeding them, and that data moves through pipelines drawing from cloud sources, data lakes, and large language models at a speed traditional controls were never built to match.
The risk is already visible in the numbers. The 2025 breach cost report found that 63% of breached organizations lacked AI governance policies, and only 37% had approval processes or oversight in place. Shadow AI, the unsanctioned use of AI tools, was a factor in 20% of breaches. The pattern matches the retrofit problem exactly. Adoption outran governance, and exposure followed.
Amiseq extends the same life cycle discipline into AI data pipelines. Discovery, classification, monitoring, and remediation carry into the data that trains and serves models, with centralized security and governance policies enforced throughout AI development and deployment. Data feeding a model gets the same protect, tag, dispose, and report treatment as any other sensitive asset, so governance keeps pace with AI innovation instead of trailing it.
Build Protection In From Day One
Data security engineering is a delivery capability, not a tool deployment. Tools enforce controls, but the protection comes from how the data life cycle is designed, built, and operated. Buying a platform does not build the discipline. Engineering it into the way data is handled does.
The difference shows up in the outcomes that matter to the CISO, the CIO, and the data leaders who answer for both risk and velocity: fewer incidents, lower remediation cost, faster teams, and AI pipelines governed from the first dataset forward.
Amiseq builds that discipline into the life cycle, from the dataset build to disposal, across enterprise and AI data alike. To engineer protection into your data from day one, talk to our data security team.
Related Blog
Transformation enabled
While most of the organizations fast track digital transformation, it is essential to consider...
BPA Total Cost of Ownership Video Series
Making sense of the Total Cost of Ownership is a prerequisite for producing above average...
Making Sense of the Total Cost of Ownership – Assessment & Consulting | Development & Deployment
Assessment and consulting costs are the costs of engaging a suitable BPA third-party...