Blog
Five Days to Under Two Hours: What Deployment Speed Does to Your Risk Window
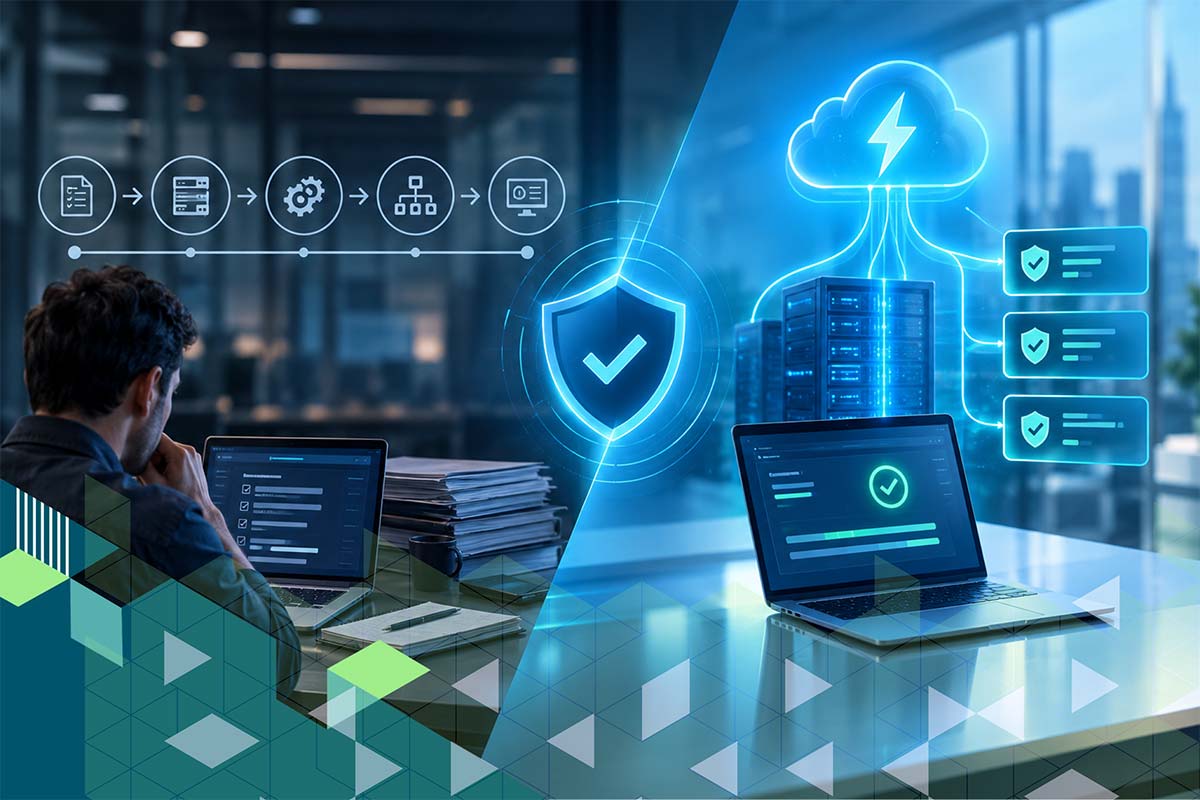
Every security control an enterprise buys carries a second price that never appears in the contract. The first price is the platform. The second is the interval between the signature and the first working scan, paid in exposure the organization has already identified and already funded a fix for.
Budget reviews capture the first number. Deployment time sits on an implementation plan as project overhead, owned by professional services and tracked against a delivery date. Measured against attacker behavior, it reads differently. Every day a control spends in deployment is a day of known, unclosed exposure, documented in the risk register and visible to everyone involved.
Security Tool Deployment Time Is Unclosed Exposure
The exploitation of vulnerabilities became the most prominent initial access vector in breach data for 2025, reaching 31% of breaches and climbing from 20% a year earlier, according to the Verizon Data Breach Investigations Report.
Attackers work against the same calendar as the implementation team, and they are not waiting for a go-live date. A control still in deployment produces no telemetry, blocks nothing, and reports on nothing. The window between purchase and protection is exposure the organization can already describe in detail, which makes it harder to defend to a board or an auditor than a weakness nobody knew about.
Time-to-Protection Shapes Security Outcomes More Than Tool Selection
Verizon's breach data also tracks what happens once a vulnerability is known. Enterprises fully remediated only 26% of the vulnerabilities in the CISA Known Exploited Vulnerabilities catalog during 2025, down from 38% the year before, and median time to full resolution reached 43 days, close to two weeks longer than the previous year’s 32.
Remediation clocks depend on detection, and detection depends on deployed tooling. A vulnerability sitting in an environment with no scanner running stays invisible, which means the 43-day median starts late for every organization still in rollout. Deployment latency compounds into remediation latency, and the combined figure determines how long an exploitable weakness stays available to anyone looking for it.
Evaluation cycles rarely account for any of it. Months go into feature comparison, proof-of-concept scoring, and reference calls, while the question of how long the winning product takes to reach a working state goes unasked. Time-to-protection connects the tooling decision to a security outcome, which earns it a place in the evaluation criteria alongside detection coverage and integration depth.
What Manual Security Deployment Costs Beyond the Calendar
Manual deployment of an enterprise security platform runs through five stages:
- Prerequisites validation
- Infrastructure deployment
- Application installation
- Initial setup, covering IP and hostname customization, license updates, and integration with adjacent components
- Baseline configuration, covering scan policies and dashboards
Each stage opens only after the one before it closes, and each needs a certified engineer on hand. Five days is what the sequence costs when every stage gets that engineer the moment it needs one. Rollouts compete for those specialized resources with every other project in the queue, so the working timeline usually stretches further. Regions without local certified engineers wait longest, which turns geography into a security variable.
Manual configuration introduces variance as well. Two deployments of the same product, run by two engineers, produce two different baselines, and the differences surface later as inconsistent scan coverage or dashboards reporting on different things. Proof-of-concept work carries the same drag, where a setup measured in days pushes the evidence a buyer needs further out and stalls the decision.
The Tenable Vulnerability Management Deployment Result: Five Days to Under Two Hours
Z-Deploy reduced Tenable Vulnerability Management deployment from five days to under two hours.
Converted into exposure time, the change removes roughly 118 hours of unclosed risk from a single deployment. One environment gains back most of a working week of protection. A financial services firm rolling the same platform into twelve regional sites recovers close to sixty days of aggregate exposure across the program.
Downstream effects follow the same curve. Scan policies and dashboards run on day one, so the remediation clock starts days earlier against a median that has already stretched to 43 days. Proof-of-concept cycles compress from a week to an afternoon, which shortens sales cycles for product vendors and shortens decision cycles for the enterprises evaluating them.
How Zero Touch Deployment Automation Closes the Risk Window
Z-Deploy automates setup, configuration, and delivery through a Zero Touch Intelligent Automation module operated by a digital workforce. Automated procedures handle the stages that consume the manual timeline, and the deployment runs without the certified engineer the manual path requires.
Products reach the platform through a controlled onboarding path. The Amiseq Intelligent Automation workforce builds the deployment module, subject-matter experts and product specialists validate and test it, and the published module becomes available to professional services teams and system integrators. The validation step is what allows a two-hour deployment to produce a baseline an enterprise can trust.
Coverage spans on-premises, cloud, hybrid, and air-gapped environments, with a standalone version for air-gap deployments where connectivity constraints usually add days to a manual timeline. Consistency comes built in: every deployment of a given product produces an identical configuration, which removes the manual error behind inconsistent security baselines across sites.
Treating Deployment Speed as a Security Requirement
Three questions belong in every security tooling evaluation. How long from contract signature to first working scan or first enforced policy? Which prerequisites fall to the buyer, and how long do they take to satisfy? Does the deployment repeat identically across sites and regions, or does each one depend on who runs it?
For most organizations, the fastest available security improvement is a shorter interval between the purchase and the protection.
Related Blog
Transformation enabled
While most of the organizations fast track digital transformation, it is essential to consider...
BPA Total Cost of Ownership Video Series
Making sense of the Total Cost of Ownership is a prerequisite for producing above average...
Making Sense of the Total Cost of Ownership – Assessment & Consulting | Development & Deployment
Assessment and consulting costs are the costs of engaging a suitable BPA third-party...